Methodology
StructureClerk assesses organizational compliance across four complementary domains: personal data protection, artificial intelligence governance, cybersecurity, and algorithmic compliance.
Approach
The 200+ question questionnaire is built from the official regulatory texts of 192 jurisdictions. Each question is mapped to the specific requirements of the applicable frameworks, enabling cross-assessment when an organization operates in several markets at once.
The assessment produces a score by domain and by jurisdiction, identifies priority gaps, and generates a professional-grade PDF report immediately usable by compliance, legal or executive teams.
Four domains
Data protection
GDPR, Law 25, PIPEDA, CCPA, LGPD, PIPL and national frameworks
AI governance
EU AI Act, C-27, sectoral guidelines
Cybersecurity
NIS2, CIRCIA, ISO 27001, NIST CSF 2.0
Algorithmic compliance
EU AI Act, Law 25, transparency, audit and traceability
Canadian legal framework (annex)
This section details the Quebec and Canadian instruments, the corpus this methodology was first built on. It is an annex, not the scope of the method: the coverage table below states what the dataset holds for every other jurisdiction.
Data protection
Law 25 — Act to modernize legislative provisions as regards the protection of personal information
RLRQ c P-39.1 · Quebec · Private sector · In force: September 2022 to September 2024, phased
Act respecting access to documents held by public bodies and the protection of personal information
RLRQ c A-2.1 · Quebec · Public sector · In force: 1982 · amended 2006, 2021-2024
PIPEDA — Personal Information Protection and Electronic Documents Act
L.C. 2000, c. 5 · Canada (federal) · Private sector, commercial activities · In force: 2000 · amended 2015, 2018
Privacy Act
L.R.C. 1985, c. P-21 · Canada (federal) · Government institutions · In force: 1983
AI governance
Indication IA-RI-2025-003-OP
IA-RI-2025-003-OP · Québec Ministry of Cybersecurity and Digital Technology · Quebec · Public sector · Compliance required by June 5, 2026
Directive on Automated Decision-Making
Treasury Board of Canada · Canada (federal) · Federal institutions · In force: 2019
Cybersecurity
LGGRI — Act respecting the governance and management of information resources
RLRQ c G-1.03 · Quebec · Public sector · In force: 2011 · amended 2021, 2023
Act respecting the Ministère de la Cybersécurité et du Numérique
RLRQ c M-17.1.1 · Quebec · Public sector · In force: 2021
Algorithmic compliance
Law 25, automated decision provisions (s. 12.1)
RLRQ c P-39.1 · Quebec · Private sector · In force: September 2023
Texts under consideration, not yet in force: C-8 (critical systems cybersecurity), second reading ; C-27 / LIAD (artificial intelligence and data), died on the order paper, January 2025
Regulatory sources
- Regulations and directives: GDPR, AI Act, NIS2, Law 25, PIPEDA, CCPA, LGPD, POPIA, NDPA, PIPL, and the data protection regimes in force in 168 jurisdictions
- International standards: ISO 27001, NIST CSF 2.0, SOC 2
- Supervisory authority guidelines: CNIL, OPC, ICO, CISA, ENISA, and others
Coverage
192 jurisdictions across 8 regions:
Depth by domain
| Domain | Jurisdictions mapped |
|---|---|
| Data protection, law in force | 168 |
| Data protection, regime in progress | 24 |
| AI governance | 18 |
| Cybersecurity | 5 |
Oldest verification in the dataset: 2025-01-31. Most recent: 2026-07-12. Every authority API decision publishes the verification date of each law it cites, along with the oldest of them.
Two verification tiers
The jurisdictions the authority engine actually decides on: cross-border transfer regime, localisation duty, right to human involvement. Re-verified every cycle. We re-verify what we decide on.
Sourced coverage, useful for knowing that a regime exists, but no decision is staked on it. Re-verified less often, and every citation carries its own date.
Regulatory monitoring process
Legislative changes are detected through the official sources of supervisory authorities (CNIL, OPC, ICO, CISA, ENISA and others), the official gazettes of covered jurisdictions, and the publications of standardization bodies (ISO, NIST). Monitoring prioritises the jurisdictions the engine decides on, re-verified every cycle. The remaining jurisdictions are indicative coverage and are re-verified less often: the last-verified date of each law is published with every citation rather than promised. The oldest in the dataset goes back to 2025-01-31.
The author
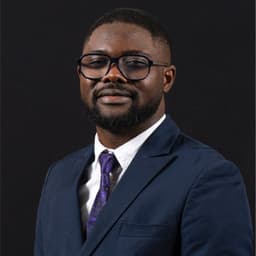
Michel Fotsing is a cybersecurity architect, CISSP, ISO/IEC 42001 Lead Auditor, and a member of the ISC2 Exam Review Commission. He is the author of L'Architecte Numérique and publishes the newsletter of the same name.
Limitations
StructureClerk is a decision-support tool. The report results identify potential gaps and guide action priorities. They do not constitute legal advice and do not replace the expertise of a legal counsel or a certified auditor for final compliance decisions.